
Cybersecurity Act (Croatia) For MSPs And
MSSPs — And Their Clients
Deliver scalable compliance services aligned with Croatia’s Cybersecurity Act using Cynomi’s AI-powered vCISO platform. Automate risk assessments, generate required documentation, and help essential and important entities meet their obligations with confidence.
What is the Cybersecurity Act and Why
Does It Matter for MSPs and MSSPs?
Croatia’s Cybersecurity Act (Zakon o kibernetičkoj sigurnosti) is the national law transposing the EU NIS2 Directive. Among the first NIS2 transpositions in the EU, it requires essential and important entities across critical sectors to implement cybersecurity risk management measures, report significant incidents on strict timelines, and submit to national registration and supervision.
For MSPs and MSSPs, the Act dramatically expands the regulated market in Croatia. Thousands of mid-sized companies are in scope for the first time, and most lack the internal security expertise to classify themselves, close gaps, and stand up the required processes. Providers can package readiness assessments, policy development, incident response preparation, and ongoing compliance management as recurring services.
What Organizations Does
the Cybersecurity Act Apply To?
The Act applies to essential and important entities in Croatia across the sectors defined by NIS2. It is especially relevant for:

Energy, Transport, and Utility Operators

Healthcare and Pharmaceutical Organizations

Banking and Financial Market Infrastructure

Digital Infrastructure and ICT Service Providers

Manufacturing, Food, and Postal Sector Companies

MSPs and MSSPs Serving Croatian Clients
Cybersecurity Act Core Components
The Act follows the NIS2 structure, scaled to Croatia’s national cybersecurity system. Core components include:

Entity Classification
Organizations are categorized as essential or important based on sector, size, and criticality, with obligations scaled accordingly.

Risk Management Measures
Required policies covering risk analysis, incident handling, business continuity, cryptography, and cyber hygiene.

Incident Reporting
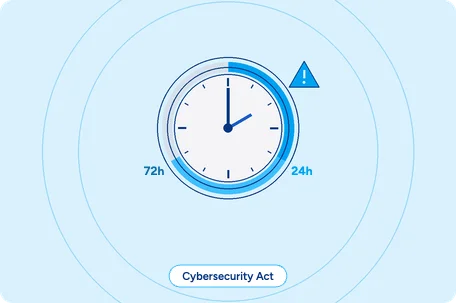
Significant incidents require an early warning within 24 hours, a notification within 72 hours, and a final report.

Management Accountability
Leadership must approve cybersecurity measures, oversee implementation, and complete training.

Supply Chain Security
Entities must assess and manage cybersecurity risks across their suppliers and service providers.

Supervision and Enforcement
Registration, self-assessment, audits, and financial penalties for non-compliance.
Why MSPs and MSSPs Should
Align With the Cybersecurity Act
Aligning with the Act enables providers to capture a newly regulated market while reusing a methodology that transfers across every NIS2 country.
Deliver structured, NIS2-aligned compliance services to newly in-scope Croatian companies
Help clients meet classification, risk management, and incident reporting obligations
Turn one-time readiness projects into recurring compliance and oversight programs
Reuse one delivery methodology across NIS2 transpositions in every EU market you serve
How MSPs and MSSPs Can Comply with the
Cybersecurity Act and Help Clients Do the Same
Cynomi guides you step by step through managing cybersecurity and compliance.
Assess & Identify
Launch Assessments Aligned With the Act’s Requirements
- Conduct automated gap assessments across the required risk management measures
- Help clients determine their classification and the obligations that apply
- Generate risk scores and prioritized findings for each entity
Establish and Plan
Build the Required Policies and Response Capabilities
- Auto-generate policies covering risk analysis, incident handling, continuity, and supply chain security
- Map remediation owners, timelines, and priorities into a clear roadmap
- Prepare incident response procedures that meet the 24-hour and 72-hour reporting deadlines
Optimize and Track Progress
Maintain Compliance and Demonstrate It
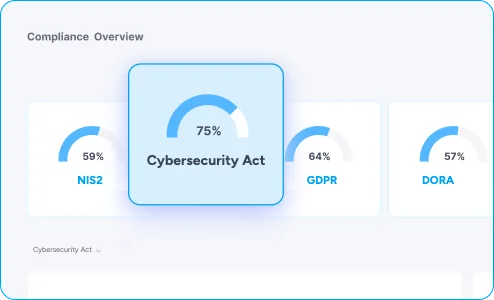
- Track progress by requirement area across all Croatian clients in one dashboard
- Maintain documentation and evidence ready for supervision and audits
- Deliver executive-ready reports that keep management informed and accountable
Framework FAQs
Yes. Essential and important entities in Croatia must comply, including registration, risk management measures, and incident reporting obligations.
It is Croatia’s national transposition of the EU NIS2 Directive — one of the first in the EU — implementing the directive’s requirements through Croatian law and national supervision.
Following the NIS2 model: an early warning within 24 hours of becoming aware of a significant incident, an incident notification within 72 hours, and a final report after the incident is handled.
The Act follows NIS2’s penalty framework, with substantial fines scaled to the entity’s classification and turnover, alongside supervisory measures and management accountability.
Cynomi automates assessments aligned with the Act’s requirements, generates policies, tracks remediation, and maintains audit-ready documentation — enabling MSPs and MSSPs to deliver NIS2 compliance services across Croatian clients at scale.