
CyFun 2025 For MSPs And
MSSPs — And Their Clients
Deliver scalable, CyFun-aligned cybersecurity services with Cynomi’s AI-powered vCISO platform. Automate assessments across assurance levels, generate policies, and help Belgian clients build resilience and demonstrate NIS2 conformity.
What is CyFun 2025 and Why
Does It Matter for MSPs and MSSPs?
CyFun 2025 is the latest release of the CyberFundamentals Framework developed by the Centre for Cybersecurity Belgium (CCB). It provides organizations with a set of concrete, prescriptive security measures drawn from established standards — NIST CSF, ISO 27001, CIS Controls, and IEC 62443 — organized into assurance levels that scale with an organization’s size and risk exposure. The 2025 release aligns the framework with NIST CSF 2.0 and with the requirements of Belgium’s NIS2 law, where CyFun serves as a recognized path to demonstrate conformity.
For MSPs and MSSPs, CyFun is a ready-made service blueprint for the Belgian market. Its assurance levels let providers right-size security programs for everything from small businesses to essential entities, and its role in NIS2 conformity means demand is driven by regulation, not just good intentions.
What Organizations Does
CyFun 2025 Apply To?
CyFun is designed for organizations of any size that want to strengthen resilience, and it carries particular weight for entities regulated under Belgium’s NIS2 law. It is especially relevant for:

Essential and Important Entities Under Belgium’s NIS2 Law

Small and Mid-Sized Businesses Building a Security Baseline

Manufacturing and Industrial Companies

Healthcare, Energy, and Transport Operators

Suppliers and Service Providers to Regulated Entities

MSPs and MSSPs Serving Belgian Clients
CyFun 2025 Core Components
The framework combines a risk-scaled structure with concrete, auditable measures. Core components include:

Assurance Levels
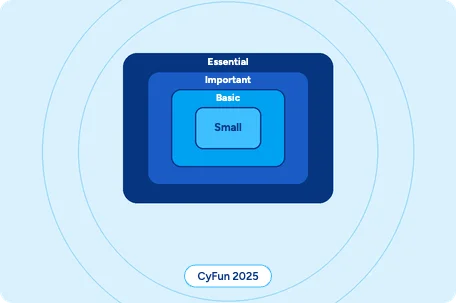
Progressive levels (Small, Basic, Important, Essential) that scale controls to the organization’s size and risk exposure.

Function-Based Structure
Controls organized around the NIST CSF functions, aligned with CSF 2.0 in the 2025 release.

Concrete Security Measures
Prescriptive requirements drawn from NIST CSF, ISO 27001, CIS Controls, and IEC 62443.

Risk-Based Level Selection
A risk assessment determines which assurance level fits each organization.

Self-Assessment and Verification
Conformity can be self-assessed or independently verified for a recognized CyFun label.

NIS2 Conformity Path
In Belgium, CyFun serves as a recognized mechanism for demonstrating NIS2 conformity.
Why MSPs and MSSPs
Should Align With CyFun 2025
Aligning with CyFun enables providers to deliver right-sized, regulation-backed security programs across the Belgian market.
Deliver standardized services with a framework that scales from SMEs to essential entities
Help clients demonstrate NIS2 conformity through a recognized national mechanism
Turn assurance-level progression into a natural upsell path as clients mature
Support cross-mapping to NIST CSF, ISO 27001, and CIS Controls without duplicate work
How MSPs and MSSPs Can Comply with
CyFun 2025 and Help Clients Do the Same
Cynomi guides you step by step through managing cybersecurity and compliance.
Assess & Identify
Launch CyFun-Aligned Assessments at the Right Level
- Conduct automated assessments aligned with the client’s assurance level
- Identify gaps against the framework’s concrete measures
- Generate risk scores and prioritized findings for each client
Establish and Plan
Build Programs That Progress Through the Levels
- Auto-generate policies and remediation plans mapped to CyFun requirements
- Map owners, timelines, and priorities appropriate to each client’s level
- Plan the path from baseline levels toward higher assurance as clients mature
Optimize and Track Progress
Maintain Conformity and Demonstrate It
- Track progress across all Belgian clients in one dashboard
- Maintain documentation and evidence to support verification and labeling
- Deliver executive-ready reports that show resilience improving over time
Framework FAQs
No. CyFun is voluntary, but in Belgium it serves as a recognized way to demonstrate conformity with the NIS2 law — which is mandatory for essential and important entities.
The Centre for Cybersecurity Belgium (CCB), the national authority for cybersecurity, which also oversees Belgium’s NIS2 implementation.
The framework defines progressive assurance levels — Small, Basic, Important, and Essential — so organizations implement measures proportionate to their size and risk exposure. Each level builds on the previous one: Basic covers essential hygiene controls, while Important and Essential add progressively more advanced measures for higher-risk and critical entities.
Its measures are drawn from and mapped to NIST CSF, ISO 27001, CIS Controls, and IEC 62443, so work done for CyFun translates directly to other frameworks clients may need.
Cynomi automates CyFun-aligned assessments, generates policies, tracks remediation, and maintains the documentation clients need for self-assessment or verification — enabling MSPs and MSSPs to deliver the framework at scale.